


 Password Manager
 Identity Theft Protection

 Team / Business
 Enterprise
 Government
 MSP

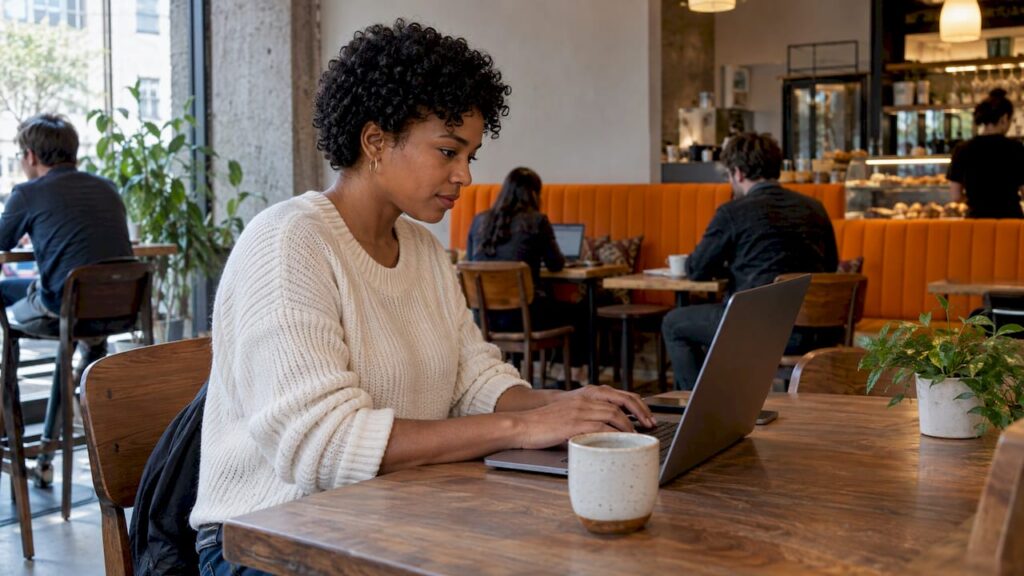
A VPN is worth using on public Wi-Fi when you don’t know who runs the network. It encrypts the traffic between your device and the VPN provider, so the hotspot owner and anyone snooping on that network see far less. But a VPN covers only one risk: your traffic being read in transit. The thing attackers actually want is your login, and that is protected by strong unique passwords, passwordless multi-factor authentication (MFA) and monitoring for leaked credentials. Together, these layers mean a bad hotspot has little to steal.
This guide is for everyone who connects away from a trusted network: individuals, small and medium businesses, large enterprises, government agencies and managed service providers (MSPs, the firms that run IT for other companies). It explains what a VPN does, what it can’t do, and how to build a setup that holds up at an airport, a hotel or a coffee shop.
TL;DR
- A VPN encrypts your connection to the VPN provider, which hides your traffic from the hotspot operator and others on the network. It is most useful on networks you don’t trust.
- Most major sites now use HTTPS, so a VPN is an extra layer for many everyday tasks rather than the only protection. It matters more for unencrypted traffic and for hiding where you connect.
- A VPN does not stop phishing, malware or tracking, and the VPN provider can see your traffic, so provider choice is a security decision.
- Your accounts are the real target. Unique passwords from a password manager, passwordless MFA and dark web monitoring protect you on any network, with or without a VPN.
- For banking or Social Security numbers, a phone hotspot is the safer route than public Wi-Fi.
What actually happens on public Wi-Fi
Public Wi-Fi is a network run by someone you don’t know, shared with strangers, usually with no strong encryption between you and the router. Three things can go wrong.

Eavesdropping. Anyone on the same open network can try to capture the wireless signals your device sends. Canada’s Get Cyber Safe program lists eavesdropping to collect personal information and login credentials as a core public Wi-Fi risk.
Fake hotspots. An “evil twin” is a hotspot named to look like the real one, such as the café’s name with a small change. The same guidance says to confirm the exact network name with the venue before you join.
Other devices on the network. Malware can spread to out-of-date devices on the same network, which is why updates and a running firewall matter before you connect.
None of these require a sophisticated attacker. They require only that you join a network without checking it and then sign in to something.
How a VPN protects you there
A virtual private network creates an encrypted tunnel from your device to a server run by the VPN provider. Everything you send goes through that tunnel, so the hotspot, and anyone watching it, sees scrambled data headed to one destination.
New Jersey’s state cybersecurity office advises VPNs on unsecured or public networks because they encrypt data and use virtual IP addresses, so internet providers and threat actors can’t see your browsing activity. Its example is a coffee-shop user whose bank login and credentials could be intercepted without one.
Consumer Reports explains the practical effect: a properly configured VPN hides your network activity, including messaging and app use, from your internet provider and anyone it shares data with. Matthew Green of the Johns Hopkins Information Security Institute told the magazine that unencrypted sites and side-channel data can leak out, and a VPN wraps all that up for the coffeehouse situation.
That is the case for a VPN: it closes off a whole category of snooping in one step, regardless of which app or site you use.
Do you still need one now that most sites use HTTPS?
HTTPS is the padlock-style encryption between your browser and a website. Because most major sites use it, someone on the same network generally can’t read your passwords, messages or payment details. The security firm Pen Test Partners describes HTTPS as already preventing that kind of reading, which makes a VPN an extra layer for most everyday users instead of an absolute requirement.
The Electronic Frontier Foundation’s Surveillance Self-Defense guide makes a similar point: a VPN can protect unencrypted traffic on a public network, but with most web traffic now encrypted it is no longer a standard recommendation for everyone. It adds that VPN software should be kept updated, because a flaw such as TunnelVision can stop a VPN from protecting you.
What HTTPS leaves visible is the metadata: which domains you connect to, when, and roughly how much data moves. A VPN hides that from the local network. That is the layer a VPN adds, and it is a real one.
When a VPN earns its place
- You are on a network you don’t trust and don’t know who runs it. The EFF says a trusted VPN may be useful when you are unsure who operates the Wi-Fi.
- You work with sensitive business data away from the office and want the local network to see as little as possible.
- You use older apps or services that may not encrypt everything.
- You travel often and want one consistent habit instead of judging each network.
When HTTPS and good habits already do most of the work
- Quick browsing of well-known sites on a hotspot you have verified with the venue.
- Using apps that encrypt their own traffic, on a device that is fully updated.
Either way, the sensible approach is to treat the VPN as one layer and make sure the layers around it are in place. Our own explainer on VPN security for users and IT teams covers where a VPN helps on Wi-Fi and where other controls take over.
What a VPN does not protect you from
This is where most advice stops too early. A VPN protects your traffic in transit. It does not protect you from what happens at either end of the tunnel.
Phishing. A malicious hotspot can steer you to a convincing fake login page. Pen Test Partners notes that HTTPS cannot stop a malicious access point from sending you to a phishing site. A VPN doesn’t stop you typing your password into one either. The FBI warning relayed by Washington State’s technology agency adds that a lock icon or “https” in the address bar doesn’t prove a site is safe, since criminals now use HTTPS on malicious sites too.
Malware and ransomware. Consumer Reports quotes University of Michigan researcher Roya Ensafi: VPNs do not protect against most known online risks, such as phishing, tracking, malware and ransomware.
Tracking. The EFF is clear that a VPN is not a tool for anonymity. Companies can still track you through GPS, cookies, tracking pixels and fingerprinting.
The provider itself. Whoever runs the VPN sees your traffic. You have moved trust from the hotspot to the provider, so the choice matters.
Your device. Outdated software, unnecessary file sharing and missing updates remain exposures whichever network you use.
So the question to ask isn’t only “do I need a VPN?” It’s “if my traffic is read or my login typed into a fake page, what does the attacker get?” That question points straight to account security.

Choosing and configuring a VPN well
If you decide to use one, these points keep it working for you.
- Prefer a paid, reputable provider with a clear privacy policy. New Jersey’s guidance warns against free VPNs that collect, store and sell user data, may not secure data sufficiently, may not validate their code or may resell your bandwidth.
- Keep it updated. The EFF notes that unpatched VPN software can fail in rare public-network attacks.
- Check permissions. Remove any app permissions the VPN doesn’t need.
- Turn on a kill switch if available. It blocks traffic if the tunnel drops, so nothing travels unprotected.
- For organizations, standardize. Give staff one approved VPN configuration, so IT can manage it and support it, rather than letting each person pick an app.
A layered setup for public Wi-Fi
Here is the routine we recommend, in the order it protects you.
Before you connect
Confirm the network name with staff at the venue, since fake hotspots copy real names. Our guides on airport Wi-Fi passwords and airport network passwords show how to check what you’re joining. Update your operating system and apps, and keep your firewall on, as Get Cyber Safe advises.
While connected
Use a VPN if you don’t trust the network. Skip sensitive tasks. Washington State’s guidance says that even with a VPN, accessing bank accounts or Social Security numbers on public unsecured networks is not recommended, and it suggests a smartphone hotspot for financial transactions. Your phone’s cellular connection is a network you control.
So a stolen login is worthless
This is the layer that works whether or not the VPN does.
- Unique, long passwords for every account. If one is captured on a bad network, it opens one door only. A password manager creates and fills these so you never type them on a suspicious page.
- Passwordless MFA or strong two-factor authentication. If there is no typed password to steal, or a captured password isn’t enough alone, an intercepted login fails at the second step. Our overview of passwordless MFA and two-factor authentication explains the options, and examples of passwordless MFA show what it looks like day to day.
- Dark web monitoring. If credentials do leak, from a hotspot or anywhere else, you want to know quickly. Dark web scanning shows what turns up and what to do next.
- Account freeze. Locking down accounts you aren’t using narrows what an attacker can reach. See four ways to use account freeze.
Your own Wi-Fi at home or the office
Public Wi-Fi isn’t the only network that matters. Use strong Wi-Fi encryption and a long, random password; our guide to a random Wi-Fi password generator covers it, and the risks of skipping a WPA password are worth reading for anyone who runs a network.
What this means for each type of reader
| Reader | Main exposure on public Wi-Fi | What to put in place |
|---|---|---|
| Individual or family | Reused passwords, fake hotspots, phishing pages | Password manager, MFA, dark web monitoring, phone hotspot for banking |
| Small or medium business | Staff signing in to company tools from cafés and airports | Shared password vault, MFA enforced for everyone, one approved VPN setup |
| Large enterprise | Many devices, many networks, uneven habits | Single sign-on, passwordless MFA, central policies, managed VPN |
| Government agency | Sensitive data, strict compliance expectations | Centralized identity management and MFA with auditable access |
| MSP | Many client environments with different risks | One management console for client password and access policies |
For teams, the lesson is the same as for individuals: don’t depend on every employee making the right call on every network. Make the safe path the default. Our piece on increasing remote work security covers how to set that up for distributed staff.
Our perspective
We see public Wi-Fi as a login problem more than a network problem. A VPN is a sensible layer when you don’t trust the hotspot, and we’d encourage anyone who travels to use a reputable one. But the VPN only protects the road. What matters is what you carry on it.
If every account has its own strong password, and the sign-in needs more than that password, then a captured login stops being a disaster. That is why LogMeOnce is built around passwordless MFA, a password manager, single sign-on and dark web monitoring for individuals, businesses, enterprises, government agencies and MSPs. Each of those closes a gap that a VPN leaves open: phishing pages, reused passwords and leaked credentials.
Our advice is simple. Use a VPN on networks you don’t trust, keep your devices updated, move sensitive transactions to your phone’s connection, and make your identity the strongest thing you carry.
Mike
Put the identity layer in place
LogMeOnce offers the password and identity tools described above. The Premium plan is $0.00 per month, Professional is $2.50 per month, Ultimate is $3.25 per month and Family is $4.99 per month. For monitoring, Dark Web Monitoring is $1.67 per month and Family Dark Web Monitoring is $3.34 per month. For organizations, Teams is $4.00 per month per user and Business is $7.99 per month per user, and Enterprise is available with no published price. You can compare plans on the personal pricing page or the business pricing page, or see the full range of password and identity products.
If you manage a team or client accounts, start with our identity protection and dark web monitoring page to see how credential monitoring fits next to MFA and password management.
FAQ
Is a VPN necessary on public Wi-Fi?
Not always, but it is a useful layer. Most major sites use HTTPS, which already protects passwords and payment details from others on the network. A VPN adds protection for metadata and unencrypted traffic, and it makes the most sense on networks you don’t trust. Pair it with unique passwords and MFA.
What can a VPN not protect me from?
A VPN does not stop phishing, malware, ransomware or tracking through cookies, GPS and fingerprinting. It also doesn’t hide your traffic from the VPN provider itself. That is why a password manager and MFA are the companion measures to a VPN.
Are free VPNs safe for public Wi-Fi?
Free VPNs vary widely. New Jersey’s cybersecurity office warns that some collect and sell user data, may not secure traffic well or may resell your bandwidth. A reputable, paid provider with a clear privacy policy is the safer choice, and it should be kept up to date.
Is it safe to bank on public Wi-Fi with a VPN?
Washington State’s technology agency does not recommend accessing bank accounts or Social Security numbers on public unsecured networks, even with a VPN. Use your phone’s cellular hotspot for financial transactions, and sign in with MFA turned on.
How do I know a hotspot is legitimate?
Ask the venue for the exact network name and join only that one. Fake “evil twin” hotspots copy real names with small differences. Keep your firewall on and your device updated before you connect.
Sources
- Virtual Private Networks, New Jersey Cybersecurity and Communications Integration Cell
- Should You Use a VPN? Consumer Reports
- Why your data is safer than you think on public Wi-Fi, Pen Test Partners
- Choosing the VPN That’s Right for You, EFF Surveillance Self-Defense
- VPN module, EFF Surveillance Self-Defense
- Public Wi-Fi, Get Cyber Safe
- Safe Wi-Fi tips, WaTech
Recommended
- VPN Security for Users and IT Teams: WiFi Help, Not Malware Defense
- Why Use VPN: Protect Data and Ensure Privacy
- 2FA VPN


