


 Password Manager
 Identity Theft Protection

 Team / Business
 Enterprise
 Government
 MSP

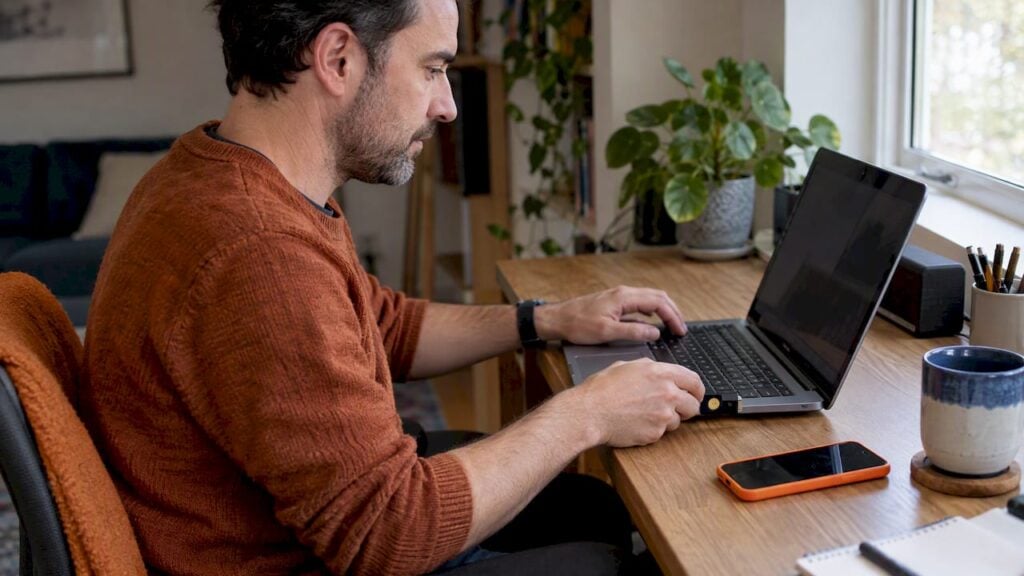
Two-factor authentication adds a second barrier so a stolen password alone won’t let an attacker in. The core advantages of two-factor authentication are fewer account takeovers, stronger resistance to phishing and credential stuffing, and easier alignment with security standards that customers and regulators expect. Some methods do this far better than others, and CISA guidance points toward phishing-resistant options as the ones worth prioritizing.
TL;DR:
- Security keys and platform authenticators using FIDO or WebAuthn bind logins to legitimate sites, while authenticator codes and push approvals remain vulnerable to user mistakes.
- SMS and email codes are the weakest common options because attackers can intercept them through SIM swaps or compromised email accounts.
- Organizations should protect email and identity accounts first, then single sign on and admin consoles, followed by financial systems and customer data.
- Recovery flows and backup codes need the same scrutiny as login controls, and teams should test fallback behavior to prevent access when MFA fails.
- NIST AAL2 calls for proof of possession and control of two distinct factors, helping teams identify systems that need stronger protection.
1. Top Benefits of Two-Factor Authentication
The case for enabling 2FA comes down to a short list of practical wins that individuals and security teams both rely on.
- Blocks stolen-password attacks: even when a password leaks in a breach, an attacker still needs the second factor to get in.
- Cuts account takeover and its fallout: fewer compromised accounts mean less identity theft, less fraud, and less time spent on recovery.
- Reduces phishing and credential stuffing success: a second factor stops many automated login attempts that rely on reused or stolen credentials.
- Builds trust with employees and customers: people feel safer using services that visibly protect their logins, which translates into fewer disputes and support tickets.
- Supports compliance expectations: frameworks referenced by agencies like NIST tie stronger authentication to higher assurance levels, which auditors and regulators increasingly expect.
- Costs less than a breach: enabling 2FA is a one-time setup cost against the ongoing cost of incident response, notification, and lost business after a compromise.
2FA stops many credential-based attacks before they start, since stolen or guessed passwords alone cannot complete a login that requires a second factor, according to FTC guidance on protecting accounts. The FTC also notes that authenticator apps and security keys hold up better than SMS codes in many situations, which matters when choosing which method to roll out first. Our practical guide to enabling 2FA walks through the setup choices in more detail for readers who want a step-by-step view.
2. How Two-Factor Authentication Works: Factors, Flows, and a Simple Example
Two-factor authentication combines two different categories of proof:
- Something you know: a password or PIN.
- Something you have: a phone, authenticator app, or physical security key.
- Something you are: a fingerprint, face scan, or other biometric marker.
Common flows include a one-time code from an authenticator app, a code sent by SMS, a push notification you approve on your phone, a physical security key you tap or insert, or a biometric scan on your device.
A typical login looks like this: you enter your username and password, the service asks for the second factor, you open your authenticator app or approve a push notification, and you’re in. Many services remember a trusted device for a set period, so you aren’t prompted every time, but they still require the second factor for new devices, password resets, or high-risk actions like changing account details.

3. How Secure Each Method Is: Phishing Resistance and a Practical Ranking
Not all second factors offer the same protection. CISA’s guidance on phishing-resistant MFA ranks methods roughly as follows, from strongest to weakest:
- Security keys and platform authenticators (FIDO/WebAuthn): cryptographically bind the login to the real website, so a fake login page simply can’t capture usable credentials.
- Authenticator app codes and push approvals with number matching: stronger than SMS but still vulnerable to a user approving a request they shouldn’t.
- SMS and email one-time codes: the weakest common option, since they can be intercepted through SIM swap attacks or redirected mail.
Phishing-resistant methods resist SIM swapping, push-bombing, and reverse-proxy phishing far better than code-based options, as CISA has documented in its work on modern MFA bypass techniques. Attackers increasingly exploit the weaker methods: flooding a user with push approval requests until one gets accepted by mistake, or intercepting a texted code after hijacking a phone number. For admin accounts, financial systems, and anything handling sensitive data, prioritizing a security key or platform authenticator closes off these common attack paths.
4. Business and Compliance Advantages
For organizations, 2FA lowers the probability of a breach and shrinks the cost of responding when something does go wrong. NIST’s AAL2 requirement calls for proof of possession and control of two distinct factors at higher assurance levels, giving security teams a standards-based way to decide which systems need the strongest protection.
Prioritize enforcement in this order:
- Email and identity provider accounts, since compromising these unlocks everything else.
- Single sign-on and admin consoles, which control access across many systems at once.
- Financial systems and anything handling customer data.
Measure success with fewer account takeover incidents and fewer fraud-related support tickets over time. Our business-focused breakdown of 2FA advantages covers rollout sequencing in more depth.
5. Implementation Best Practices and Common Pitfalls
Getting the benefits of 2FA depends on how it’s deployed, not just whether it’s turned on.
- Enforce MFA broadly, starting with privileged users and the highest-risk services before expanding to everyone else.
- Prefer phishing-resistant authenticators where available; where they aren’t, use number matching or stronger push protections instead of plain approve/deny prompts.
- Harden account recovery flows and backup codes, since attackers often target password resets and recovery questions to bypass MFA entirely, a weakness documented in the OWASP MFA cheat sheet.
- Avoid “fail open” configurations that let logins through when an MFA component is down, and test that fallback behavior before you need it.
- Plan onboarding carefully, with clear instructions and simple device enrollment so people adopt the new step instead of working around it.
Pro Tip: Treat your account recovery process with the same scrutiny as your login screen. It’s often the softer target.
A Practical Case for Moving Past Passwords Alone
Passwords were never built to stand alone, and the evidence for pairing them with a second factor is hard to argue with. My honest read after looking at the guidance from CISA, NIST, and the FTC is that the direction is clear: move toward phishing-resistant methods wherever you can, and don’t treat SMS codes as a permanent solution. Secure your recovery options with the same care as your primary login, since that’s where shortcuts tend to show up first.
— Mike
Making Strong Authentication Easier to Adopt
Choosing the right second factor is only half the job; using it consistently across every account is the other half. Our password manager pairs with passwordless MFA and single sign-on so you can enforce strong authentication across accounts without juggling separate apps for each one, and our dark web monitoring flags exposed credentials before they turn into a login attempt against you.
If you’re ready to see how these pieces fit together for your accounts or your team, compare our plans and pricing and start with the option that matches your setup.
FAQ
What are the advantages of two-factor authentication?
Two-factor authentication blocks most attacks that rely on a stolen or guessed password alone, since the attacker also needs the second factor. It also reduces phishing and credential stuffing success rates and helps organizations align with standards like NIST’s AAL2 guidance.
What are the benefits of 2FA security?
The main benefits are fewer account takeovers, less fraud-related cleanup work, and stronger protection for sensitive accounts like email and admin consoles. FTC guidance notes that authenticator apps and security keys offer better protection than SMS codes in many cases.
What is the main disadvantage of two-factor authentication?
The main friction point is added steps at login, and weaker methods like SMS codes carry risks such as SIM swap interception. Choosing a phishing-resistant method like a security key, and hardening recovery flows, addresses most of these concerns.
What is the main advantage of using multi-factor authentication?
The main advantage is that a compromised password alone no longer grants access, since a second, independent factor is also required. This single change closes off the most common path attackers use to take over accounts.
Sources
- Implementing Phishing-Resistant Multi-Factor Authentication (MFA) (CISA fact sheet)
- Digital Identity Guidelines: Authentication and Authenticator Management (NIST SP 800-63b)
- Use two-factor authentication to protect your accounts (FTC)
Recommended


