
Why Passwordless Authentication Is Safer
Passwords are the weakest link in cybersecurity. Passwordless authentication eliminates password theft, phishing, and credential breaches.
Passwords
- Phishable
- Reusable
- Forgettable
- Stealable
Passwordless
- Phishing-proof
- Unique per service
- Nothing to forget
- Nothing to steal
Why Passwords Are the Weakest Link
Passwords were designed for a simpler era. Today they are the primary attack vector for cybercriminals worldwide.
Password Reuse
Users repeat the same password across dozens of websites, creating cascading breach risks.
Phishing Attacks
Sophisticated phishing campaigns trick employees into entering credentials on fake sites.
Credential Stuffing
Automated bots test stolen credentials against thousands of services simultaneously.
Weak Passwords
Most users choose easy-to-guess passwords, with '123456' still topping the list year after year.
"Over 80% of breaches involve stolen passwords."
— Verizon Data Breach Investigations Report
Passwordless Authentication Explained
Passwordless authentication verifies identity using devices, biometrics, or secure tokens instead of passwords. No secrets are transmitted or stored on servers.
How Passwordless Login Works
User Attempts Login
Enter your email or username — no password field needed.
Request Sent to Device
A cryptographic authentication request is pushed to your trusted device.
Identity Verified
Approve with biometrics — Face ID, fingerprint, or selfie authentication.
Secure Access Granted
You're in. No password was transmitted, stored, or exposed.
Multiple Ways to Authenticate Securely
Selfie Authentication
Patented facial recognition login — snap a selfie to verify your identity securely.
Biometric Login
Use device-native biometrics like Face ID and Touch ID for instant access.
Fingerprint Auth
Leverage fingerprint sensors on any device for fast, phishing-proof authentication.
Secure PIN Backup
Set a secure PIN as a fallback when biometric authentication is unavailable.
Password Fallback
Traditional password option remains available for maximum flexibility.
Why Passwordless Security Is Stronger
Passwordless authentication doesn't just replace passwords — it eliminates entire categories of attacks.
No Password Theft
Nothing to steal — credentials never leave your device.
No Phishing
Authentication is device-bound, making phishing attacks impossible.
No Credential Reuse
Unique cryptographic keys per service eliminate reuse risks.
Stronger Verification
Multi-factor identity proof is inherent in every login.
Reduced Attack Surface
No password database means no mass credential breach.
Passwordless Security Platform
LogMeOnce delivers a complete passwordless identity security platform with patented authentication technology.
Selfie Authentication
Patented selfie-based identity verification.
Multi-Factor Auth
Layer authentication with biometrics, OTP, and device trust.
Identity Risk Scoring
Real-time risk assessment for every login attempt.
Secure Password Vault
Zero-knowledge encrypted vault for legacy passwords.
Cloud Encryption
Encrypt files across Dropbox, Google Drive, and OneDrive.
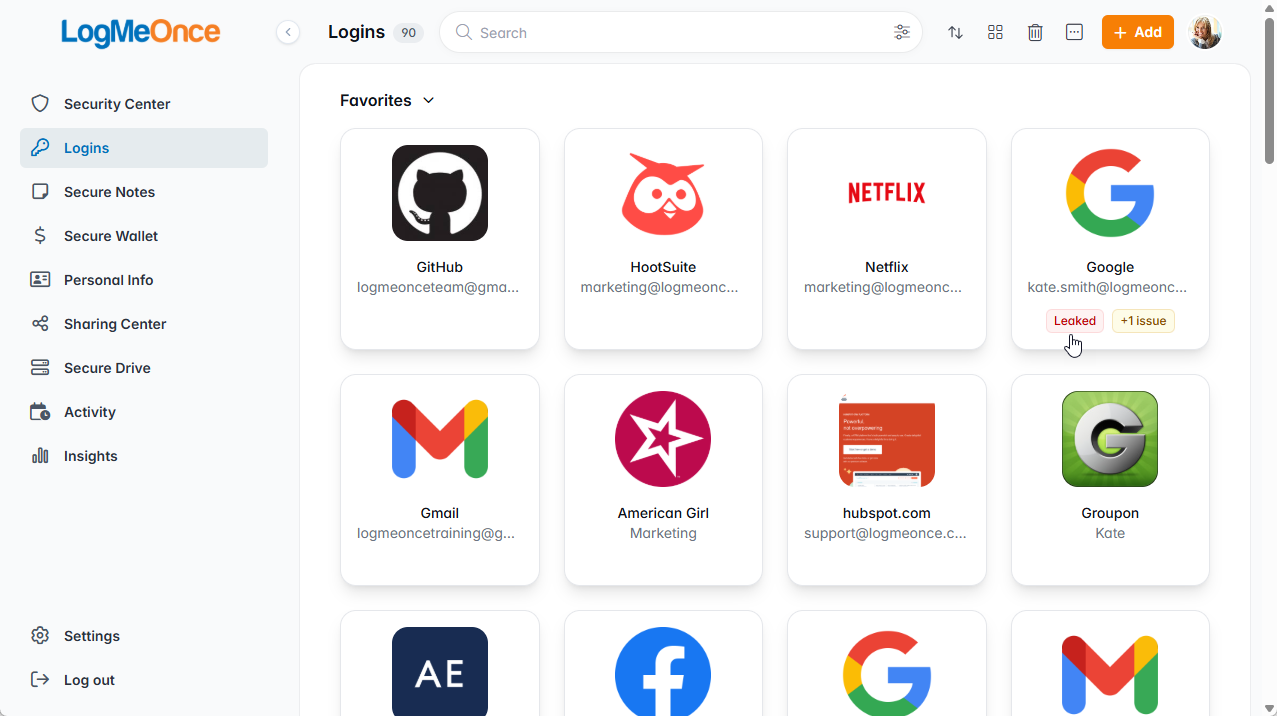
Password vs Passwordless Security
See why organizations worldwide are migrating from traditional passwords to passwordless authentication.
How Passwordless Improves Security
Reduced Security Breaches
Eliminate the #1 attack vector — stolen passwords — from your organization.
Stronger Identity Verification
Every login is backed by cryptographic proof tied to a verified device.
Lower Help Desk Costs
Password resets account for 20-50% of IT tickets. Passwordless eliminates them.
Simplified User Experience
Users log in faster with biometrics than typing complex passwords.
Trusted Security Platform Since 2012
LogMeOnce has delivered advanced identity security solutions worldwide with patented passwordless authentication and zero-knowledge encryption.
Explore Passwordless Features
Start Using Passwordless Security Today
Create a free account and strengthen your security with passwordless authentication.
