


 Password Manager
 Identity Theft Protection

 Team / Business
 Enterprise
 Government
 MSP

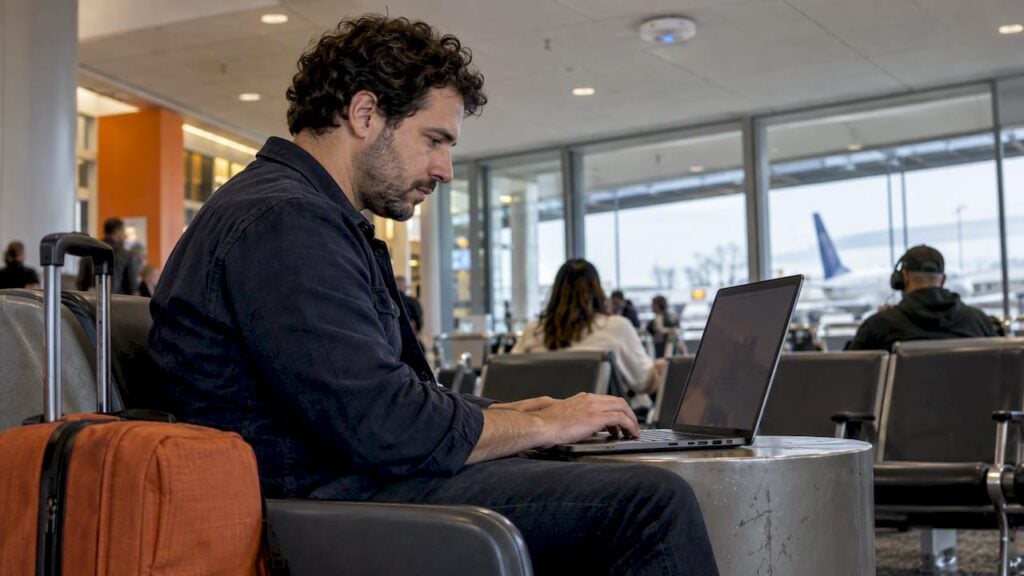
A VPN improves security for specific network-layer risks, but it is not a universal security fix. It encrypts your connection and masks your IP address, which matters most on untrusted Wi-Fi, when you want to limit what your internet provider sees, or when you need to reach region-restricted resources. It does nothing for malware, phishing, weak passwords, or browser tracking, so treat it as one layer, not the whole defense.
TL;DR:
- A VPN hides visited domains from your internet provider but transfers that visibility to the VPN provider, making audited logging practices and jurisdiction important.
- Choose a provider with WireGuard, OpenVPN, or IKEv2/IPsec, plus a kill switch, DNS leak protection, independent audits, and stable connections.
- Home users should prioritize password managers, multifactor authentication, and updates, adding a paid, audited VPN for regular public network use or regional access.
- IT teams should rapidly patch internet facing gateways, require phishing resistant multifactor authentication, restrict appliance connections, and segment access to limit a breach’s reach.
- Keep VPN access for legacy applications or limited internal tasks, while identity based access controls suit broader cloud resources and reduce network wide trust.
How VPNs work: tunneling, encryption, and IP masking
A VPN wraps your internet traffic inside an encrypted tunnel between your device and a VPN server. Anyone watching the network between you and that server, a coffee shop router, an airport hotspot, or your internet provider, sees only scrambled data and the fact that you’re connected to a VPN. They cannot see which sites you visit or what you send. The VPN server, however, can see your real traffic once it decrypts it, which is why the provider you choose matters as much as the technology itself.
IP masking works alongside encryption. Your traffic appears to originate from the VPN server’s address instead of your own, which hides your location and device from the websites you visit and shifts visibility away from your local network. Your internet provider still knows you’re using a VPN and for how long, but loses the ability to log which domains you visit. That visibility doesn’t disappear, it moves to the VPN provider, which is a central reason provider trust matters so much.
Protocol choice shapes both security and speed. WireGuard uses a smaller, modern codebase and tends to deliver faster connections with strong cryptography. OpenVPN is older, extensively audited, and highly configurable, which makes it a common default for enterprise deployments. IKEv2/IPsec handles network switches well, which suits mobile devices moving between Wi-Fi and cellular. The EFF’s guidance on choosing a VPN notes that a VPN’s core job is providing this encrypted tunnel and IP masking, nothing more, nothing less, so protocol strength and provider trustworthiness together determine how much real protection you get.

Threats a VPN meaningfully reduces
A VPN earns its keep in a specific set of situations, mostly ones involving untrusted or hostile networks.
- Public Wi-Fi eavesdropping: encryption prevents someone on the same coffee shop or airport network from reading your traffic or intercepting login sessions.
- Man-in-the-middle attempts on untrusted networks: a properly configured tunnel makes it much harder for an attacker positioned on the local network to intercept or alter your data.
- ISP-level domain visibility: your internet provider can no longer log which sites you visit, since that visibility shifts to the VPN provider.
- IP-based targeting and geo-restrictions: masking your IP reduces location-based targeting and lets you reach resources blocked to your region.
These scenarios map directly onto real situations: working from a hotel or airport, connecting to public Wi-Fi while traveling, or accessing a company resource that’s geographically restricted. Remote workers who regularly connect from coffee shops or shared networks get the clearest, most consistent benefit, since that’s exactly the threat model a VPN was built to address.
What VPNs do not protect against (real limits and common myths)
The biggest misconception about VPNs is that they function as general-purpose security tools. They don’t.
- Malware and phishing: a VPN encrypts your connection, but it won’t stop you from downloading a malicious file or entering credentials on a fake login page.
- Account credential theft: if a password is weak, reused, or phished, a VPN does nothing to prevent the account takeover that follows.
- Browser fingerprinting and cookies: sites can still identify you through device characteristics, cookies, and login sessions, regardless of your IP address.
- GPS and app-level tracking: mobile apps that request location access can still pinpoint you even while a VPN masks your network IP.
A VPN is not an anonymity tool. The EFF is explicit that VPNs protect network-layer metadata on untrusted networks but do not replace password managers, multi-factor authentication, or endpoint security, and logging into any account immediately re-identifies you to that service regardless of your IP address.
Provider-side risk is the other half of the picture. A “security” label doesn’t guarantee privacy-respecting behavior: the FTC’s complaint against Avast describes a security-branded company collecting and selling browsing data, a reminder that free VPNs in particular often monetize the very traffic they claim to protect. Jurisdiction matters too, since a provider based in a country with broad surveillance laws can be compelled to hand over logs it claims not to keep.
How to evaluate and choose a secure VPN: practical checklist
Picking a VPN comes down to verifying a short list of technical and operational signals rather than trusting marketing copy.
- Confirm modern protocol support. Look for WireGuard, OpenVPN, or IKEv2/IPsec, and avoid proprietary protocols with no public scrutiny.
- Check for a kill switch and DNS leak protection. These stop your real traffic from leaking out if the tunnel drops unexpectedly.
- Look for independent audits. A no-logs claim means little without a third-party audit report backing it up.
- Review the vulnerability disclosure policy (VDP). A published VDP signals a provider takes reported flaws seriously and fixes them on a defined timeline.
- Ask about software bills of materials (SBOM) and end-of-life (EoL) policy. These show whether a vendor tracks its own dependencies and commits to supporting its software over time.
- Consider jurisdiction and payment options. A provider in a privacy-friendly jurisdiction that accepts payment methods not tied to your identity reduces how much account linking is possible.
- Evaluate server coverage and connection stability. A VPN that drops frequently or routes through overloaded servers undermines the very protection you’re paying for.
Pro Tip: Ask any vendor directly for their most recent third-party audit report and their VDP before you commit to a plan, free trials are a reasonable way to test stability without that commitment.
Enterprise guidance: observed VPN vulnerabilities and hardening steps
VPN gateways are attractive targets precisely because they sit at the network edge with broad access behind them. CISA’s advisory on Ivanti Connect Secure and Policy Secure gateways documents threat actors actively exploiting VPN gateway vulnerabilities, warning that a single compromised appliance can hand attackers wide lateral access across a network. A separate CISA advisory on the IXON VPN client documented a vulnerability allowing command execution as root or SYSTEM, fixed only once organizations updated to version 1.4.7 or later, illustrating how quickly a trusted remote-access tool can become the point of entry.
Several operational practices meaningfully cut this risk:
- Patch VPN appliances on a prioritized, fast timeline, since internet-facing systems are the first targets once a vulnerability is public.
- Limit outbound connections from VPN appliances, a specific mitigation CISA recommends to prevent compromised gateways from reaching further into the network.
- Use low-privilege accounts for LDAP or Active Directory binds tied to the VPN, so a compromised credential doesn’t grant broad directory access.
- Require phishing-resistant MFA on all remote access systems, closing the gap that password-only VPN logins leave open.
- Apply segmentation and least privilege so a compromised gateway cannot reach every internal system, limiting the blast radius of any single breach.
Vendor selection matters as much as configuration. A published SBOM, a working VDP, and a clear EoL policy are the clearest signals that a vendor will catch and disclose problems before they become incidents, rather than after. Pairing VPN hardening with stronger remote work security practices and mobile device hygiene closes gaps that a VPN alone leaves open.
Where VPNs fit in modern security architecture: Zero Trust and alternatives
Zero Trust starts from a different assumption than a traditional VPN: no user or device is trusted by default, regardless of whether it’s inside or outside the network perimeter. NIST Special Publication 800-207 describes granting access based on identity, device posture, and continuous evaluation, rather than on the simple fact that a device has connected through a VPN tunnel. That shift reduces how much damage a single compromised credential or device can do, since access is checked continuously rather than granted once at login.
VPNs still make sense for specific, narrower jobs: reaching legacy applications that have no modern identity-aware front end, or giving a small team temporary access to one internal resource. For broader cloud access, identity-based models like Zero Trust architectures or secure access service edge (SASE) increasingly replace the all-or-nothing network access a traditional VPN grants. NIST’s own engineering guidance on secure remote access places VPNs alongside software-defined perimeters and SASE as one component among several, not a standalone answer. A practical hybrid path keeps VPNs for specific legacy needs while moving general cloud access to agent-based, identity-aware tools.

Author perspective: recommended priorities for individuals and IT teams
For most home users, a password manager, multi-factor authentication, and prompt patching close more real risk than a VPN ever will, credential theft and phishing cause far more damage than ISP-level tracking. Add a paid, audited VPN once you regularly use untrusted networks or need geo access, and treat it as a complement, not a replacement. IT teams should harden VPN appliances, enforce least privilege, and start planning a path toward identity-centric access where legacy systems allow it.
— Mike
A complementary approach: identity protection covers what a VPN can’t
A VPN protects the pipe your traffic travels through. It does nothing for the credentials you type into a login form, the phishing email that asks for your password, or the account that gets breached because the same password was reused somewhere else. That gap is exactly where identity and credential protection take over.
We offer a password manager that provides encrypted storage for credentials, helping to mitigate risks from weak or reused passwords. We provide passwordless MFA that removes passwords from the login flow entirely for supported services, reducing risk from phishing-for-credentials attacks that VPNs cannot block. Our dark web monitoring service alerts you if your credentials appear in breaches, and our cloud storage encryption helps protect files at rest as well as data in transit.
None of these replace a VPN’s job and a VPN doesn’t replace theirs. Together they cover the two halves of the problem: the network you’re connected to, and the identity that an attacker is actually after. Information on password management, passwordless MFA, and dark web monitoring, including pricing and plans for different user types, is available on our pricing and plan comparison page.
FAQ
Are VPNs actually good for security?
Yes, for specific threats: a VPN encrypts your traffic on untrusted networks and hides which domains you visit from your internet provider. It does not protect against malware, phishing, or weak passwords, so it works best alongside other security tools rather than on its own.
What is the downside of using a VPN?
A VPN shifts visibility from your internet provider to the VPN provider, so a provider that logs traffic or gets subpoenaed can expose the same data a VPN is meant to hide. Free VPNs in particular have been shown to monetize browsing data, as the FTC’s complaint against Avast illustrates, so provider trust matters as much as the technology.
Can law enforcement see through VPNs?
A VPN hides your traffic from your local network and internet provider, but it does not make you untraceable. Law enforcement can potentially obtain logs from a VPN provider through legal processes, and browser fingerprinting, account logins, and cookies can still identify a user regardless of VPN use.
Do I need antivirus if I use a VPN?
Yes, a VPN and antivirus protect different things. A VPN encrypts your network traffic, while antivirus software detects and blocks malware, which a VPN has no ability to stop once a malicious file reaches your device.
Sources
- Threat Actors Exploit Multiple Vulnerabilities in Ivanti Connect Secure and Policy Secure Gateways
- NIST Special Publication 800-207: Zero Trust Architecture
- Choosing a VPN that’s right for you (EFF)
Recommended
- How to Increase Remote Work Security to Protect Sensitive Data
- Best Cybersecurity Tools to Use In 2026
- Professional IT Security Tips Everyone Can Benefit From


